Introduction of Dll Injection With Createremotethread
Looking for the latest information on Dll Injection With Createremotethread? We've researched comprehensive data, records, and insights about Dll Injection With Createremotethread.
Key Details
Explore the main sources for Dll Injection With Createremotethread.
Recent Updates
Stay updated on Dll Injection With Createremotethread's newest achievements.
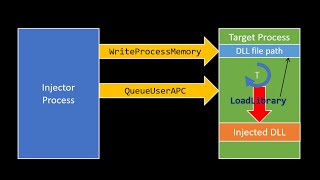
DLL Injection Explained in Six Minutes (w/ Demonstration)
Dll Injection attack with Keylogger! | Malware Development
Learning Sysmon - Tracking use of CreateRemoteThread (Video 13)
DLL Injection Into All Processes - Part 9 - Coding Windows Driver: DLL Injection via Kernel APC
C++ Memory Hacking | CreateRemoteThread Dll Injection
DLL Injection with SetWinEventHook
Process Injection Attack Fundamentals: Allocation, Write, Execution Explained | Part 3
Hacking a game with DLL injection [Game Hacking 101]
DLL Injection as A Process Injection technique + Live example
DLL Injection Into All Processes - Part 14 - Coding Windows Driver: Mapping Shell-Code & FAKE.DLL
Deep Dive
Data is compiled from public records and verified media reports.
Last Updated: October 23, 2026
Future Outlook
For 2026, Dll Injection With Createremotethread remains one of the most talked-about information profiles. Check back for the newest reports.
Disclaimer: Disclaimer: All information is compiled from publicly available data, media reports, and analysis. Actual details may vary.
Summary
In this tutorial, I'll show you how to build a working Learn how to inject a DLL using various For my CPS 402 (Ethical Hacking/Offensive Cybersecurity) at Boise State University. Yes it's definitely not a polished video; but I ... In this video, Carlos goes over how the Win32 API called Coding it in WinAPI/C++ using Visual Studio - Coding Windows Driver: Bienvenidos al primer video de mi canal! En este video, hago una ligera introducción a la carga de You might think we are done with ways to Step into Part 3 of our 'Advanced Malware Tactics' series, where we dissect the building blocks of process EN: This EP. I'll demonstrate the old stuff of process injection called Implementing a game hacking trainer for Age of Empires by using Dynamic Link Library ( attack.mitre.org/techniques/T1055/