Overview to Emotet Malware Analysis Part 2 Deobfuscating Powershell
Looking for the latest information on Emotet Malware Analysis Part 2 Deobfuscating Powershell? We've researched comprehensive data, records, and insights about Emotet Malware Analysis Part 2 Deobfuscating Powershell.
Main Features
Explore the primary sources for Emotet Malware Analysis Part 2 Deobfuscating Powershell.
Developments
Stay updated on Emotet Malware Analysis Part 2 Deobfuscating Powershell's latest milestones.
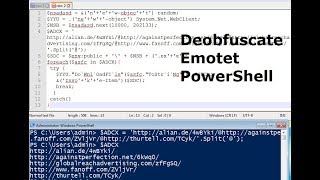
Deobfuscating emotet doc downloader
Malware Analysis - Heodo - Emotet v4 - Microsoft Word Macro
[11/10/2020] Emotet Maldoc Analysis - Embedded DLL and CertUtil for Base64 decoding (HITB CyberWeek)
Emotet Malware Analysis | MS Excel | VBScript
Emotet Malware Analysis: x32dbg Packer Analysis from Memory Dump to Binary Ninja
Malware Analysis - DOSfuscation Deobfuscation
Information Stealer - Malware Analysis (PowerShell to .NET)
Full Guide
Data is compiled from public records and verified media reports.
Last Updated: October 23, 2026
Summary
For 2026, Emotet Malware Analysis Part 2 Deobfuscating Powershell remains one of the most talked-about information profiles. Check back for the latest updates.
Disclaimer: Disclaimer: All information is compiled from publicly available data, media reports, and analysis. Actual details may vary.
Summary
In this and the next video we'll Integrate ANY.RUN solutions into your company: jh.live/anyrun-demo || Make security research and dynamic If you would to support the channel and I, Kite! Kite is a coding assistant that helps you code faster, on any IDE offer ... Earlier today (11/10/2020), AnyRun posted an DISCLAIMER: NO SOUND (Intentional) Objective is to uncover the payload and the URLs that it's retrieved from by ... Hi, This video is all about explaining "how an excel document can lead you to one of the notorious malwares ever seen? Fireeye made a white paper on cmd.exe command obfuscation (DOSfuscation). We
Emotet Malware Analysis Part 2 Deobfuscating Powershell.pdf
What is the most accurate information about Emotet Malware Analysis Part 2 Deobfuscating Powershell?
Our platform aggregates the most comprehensive and up-to-date insights, ensuring you get relevant details about Emotet Malware Analysis Part 2 Deobfuscating Powershell.
Why is Emotet Malware Analysis Part 2 Deobfuscating Powershell trending right now?
Interest in Emotet Malware Analysis Part 2 Deobfuscating Powershell has surged recently as more people seek reliable resources, related media, and detailed analysis.
Where can I find related media and updates for Emotet Malware Analysis Part 2 Deobfuscating Powershell?
You can explore extensive galleries, video summaries, and related content directly on this page.
How often is the content about Emotet Malware Analysis Part 2 Deobfuscating Powershell updated?
We regularly update our database with the latest information, media, and analysis related to Emotet Malware Analysis Part 2 Deobfuscating Powershell.