Looking for the latest information on Splunk Correlation Rule? We've compiled comprehensive data, records, and insights about Splunk Correlation Rule.
Important Facts
Explore the primary sources for Splunk Correlation Rule.
Developments
Stay updated on Splunk Correlation Rule's newest achievements.
SIEM Correlation Rules for Beginners
Splunk Tutorial for Beginners (Cyber Security Tools)
Splunk correlate Command Tutorial: Field Correlation Analysis for Beginners
Certified Splunk ES Analyst | SIEM Intelligence
How to Learn Splunk for SOC Analysts
Building Splunk Detection Rules from My Own Attack | KCD Dental SOC Investigation
Basic Searching in Splunk Enterprise
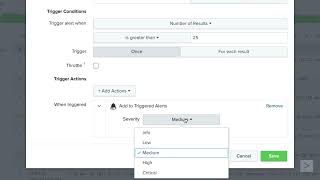
Creating Alerts in Splunk Enterprise
Splunk Webinar | FAQs | SIEM Intelligence
AI-Driven Alert Correlation with EventiQ in Splunk ITSI
Creating Advanced Alert Actions in Splunk
Detailed Analysis
Data is compiled from public records and verified media reports.
Last Updated: October 18, 2026
Conclusion
For 2026, Splunk Correlation Rule remains one of the most searched-for information profiles. Check back for the newest reports.
Disclaimer: Disclaimer: All information is compiled from publicly available data, media reports, and analysis. Actual details may vary.
Summary
How do SOC Analysts detect suspicious activity in Splunk? In this Reel, we're breaking down a L.A.M.E. Creations has scoured the internet for guidance on the Enterprise Security SIEM from Hey All! In this video, we'll be going through the basic tutorial for Build SOC Analyst Skills In 90 days Visit the MyDFIR SOC Community to find out how. skool.com/mydfir SANCLOGIC | Offense.Defense.Logic Learning to build In this video we demonstrate how to perform basic searches, use the timeline and time range picker, and use fields in the This video will show you how to create alerts in In this video, we introduce EventiQ in Want to do more with your alerts in